If gem install jekyll fails on Windows with SSL_connect or certificate verify failed, Ruby cannot validate the certificate presented by RubyGems.org. The cause is usually an outdated or missing certificate authority (CA) list, an incorrect system clock, or a network proxy that intercepts TLS. It is not a reason to turn off certificate verification or download a certificate bundle from an arbitrary source.
Check the error and your Ruby installation
Start with the exact error. A certificate-verification failure is different from a timeout, a DNS problem, or a TLS protocol error; those need different fixes. In PowerShell, check which Ruby executable is being used and which versions are installed:
where.exe ruby
ruby -v
gem --version
bundle --version
If where.exe ruby lists more than one location, make sure the first one is the installation you intend to use. An old Ruby earlier in PATH can keep using an outdated OpenSSL setup even after you install a newer version.
With a recent Bundler, run its SSL diagnostic:
bundle doctor ssl
It checks the Ruby OpenSSL setup, certificate configuration, and a test connection to RubyGems.org. You can also capture gem env when investigating a failure. Redact usernames, private paths, proxy credentials, and other sensitive values before sharing diagnostic output.
Fix common certificate failures
-
Check Windows date and time. Certificates are valid only during a defined time window. Correct the clock and enable automatic time synchronization if it is wrong.
-
Update an old Ruby installation. Use a supported Ruby+Devkit release from the RubyInstaller downloads page that meets your project's Ruby requirements, then open a new terminal and confirm
where.exe rubypoints to it. RubyInstaller releases include a Mozilla CA list; newer releases refresh that list. See the RubyInstaller FAQ and its SSL certificate notes. -
Update RubyGems when a secure connection is available. Run
gem update --systemto update RubyGems. For an existing Bundler project, update Bundler only when appropriate for that project (bundle update --bundlercan changeGemfile.lock). If the certificate error prevents these commands from connecting, updating Ruby through RubyInstaller is the safer first step; do not bypass TLS to force the update. -
Check for a custom certificate override. Ruby's OpenSSL may use
SSL_CERT_FILEorSSL_CERT_DIR. In PowerShell, inspect whether either variable is set:Get-ChildItem Env:SSL_CERT_FILE, Env:SSL_CERT_DIR -ErrorAction SilentlyContinueA stale path or incomplete CA file can replace or disrupt the certificates Ruby would otherwise use. OpenSSL documents these variables in its environment-variable reference.
-
Ask about TLS inspection on managed networks. If gem installs fail only on a work or school network, a proxy may be presenting certificates signed by an organization-specific CA. Ask the administrator for the approved CA certificate and Ruby configuration. RubyInstaller documents adding an approved PEM certificate under
<Ruby install>\ssl\certs\; do not overwrite its bundledcert.pem.SSL_CERT_FILEreplaces RubyInstaller's bundled CA list, so an override must contain every CA the connection needs, not just the organization's certificate.
If your network requires an HTTP proxy, use the address supplied by its administrator with RubyGems' --http-proxy option. Replace the sample address below with your approved proxy:
gem install jekyll --http-proxy http://proxy.company.test:8080
Retry the gem install
After correcting the clock, Ruby installation, or approved proxy/CA configuration, open a new PowerShell window and retry:
gem install jekyll
If the error persists, use the RubyGems TLS troubleshooting guide and include the sanitized output of bundle doctor ssl, gem env, and bundle env when asking for help. For a Jekyll installation overview, see the official Jekyll site and Ruby's installation documentation.
Do not disable certificate verification, switch RubyGems.org to HTTP, or install a CA file from an untrusted download. Those changes can expose gem downloads to interception.
Historical note: The screenshot below shows the system-wide
SSL_CERT_FILEworkaround from the original 2014 article. It is not the recommended fix for current RubyInstaller releases.
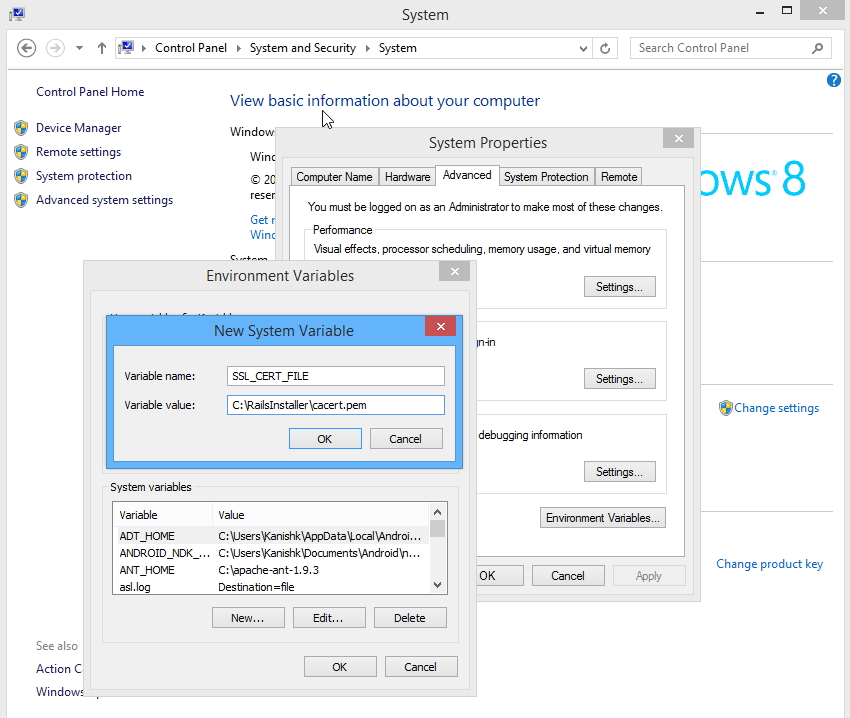
The original screenshot shows a system-wide certificate-file workaround; use the current steps above instead.

Just run
gem source –remove https://rubygems.org
to kick https source out, and leave http://rubygems.org.
While this would work, leaving out https is not really fixing the problem. Just avoiding it.
Many Thanks!
Thanks man. Lifesaver!
Thanks a lot man!, everything is working now!
You said save it to – C:RailsInstallercacert.pem
So is that path or file name and Is it necessary to save only to that path?
Hi Kiran,
That is a path and you can save it to any location. Just make sure to set the value of SSL_CERT_FILE to the location where you save the pem file.
Hello Kanishk Kunal.
when ever i run the command “gem install rails”, i always get this error.
ERROR: Could not find a valid gem ‘rails’ = 0>, here is why: Unable to download data from https://rubygems.org/ – SSL_connect returned=1 errno=0 state=SSLv3 read server certificate B: certificate verify failed
i tried out the solution you gave above but i still get the same error message. please kindly help me out.
Hi Amos,
Please make sure you have correct path set for SSL_CERT_FILE.
You can check whether you have correct environment variable set or not by running the following command in your command prompt.
echo %SSL_CERT_FILE%This should output the location where your cert files are stored.
thanks! was almost about to throw the computer into a busy street and this prevented that.
Thank you so much :)
Thanks. super helpful.
Thanks for this trick. My derivative solution for my standard ruby installation (simply installed using rubyinstaller on win10 64 bits) :
Just place the “cacert.pem” in the “rubygems/ssl_certs/” directory (in C:\ruby23-x64\lib\2.3.0 for my own installation) and that’s all.
Gelth is right just add the cacert.pem file to the existing ‘rubygems\ssl_certs’ directory of your existing ruby installation. In my case Windows 7 and installed ruby via Chocolatey the ssl certs directory of ruby by deafult is located at ‘C:\tools\ruby23\lib\ruby\2.3.0\rubygems\ssl_certs’
That’s where I added it, too.
This solved it for me too. I just saved the cert into the already existing `ssl_certs` folder.
This solution works for me as well.
Thanks, this worked great for me. Didn’t need to set any environment variables.
I didn’t find any working solution until I read your comment! Thank you so much!
Thank you! I was about to give up trying to install Jekyll on Windows when I found this. Installed! Now I can start playing.
Thanks a lot! now it works!
Thanks very very thanks
thanks buddy, saved a lot of time.
Thanks Kanishk!
Kanishk Gelth Alex thanks so much!
it works for me, very thanks
Hi I am getting the below issue
ERROR: SSL verification error at depth 2: unable to get local issuer certificate (20)
ERROR: You must add /C=US/O=BlueCoat Systems, Inc./CN=Cloud Services Root CA to your local trusted store
ERROR: Could not find a valid gem ‘compass’ (>= 0), here is why:
Unable to download data from https://rubygems.org/ – SSL_connect returned=1 errno=0 peeraddr=151.101.1.227:443 state=error: certificate verify failed (unable to get local issuer certificate) (https://rubygems.org/specs.4.8.gz)
Is there anything you can help me with
Hi.
It’s 2024 and this post is still helping us Ruby newbies. Thanks for taking the time to make it.